Digital Silence: Threat Intelligence vs. State Response in the #StopWAR Incident

Digital Silence: Threat Intelligence vs. State Response in the #StopWAR Incident

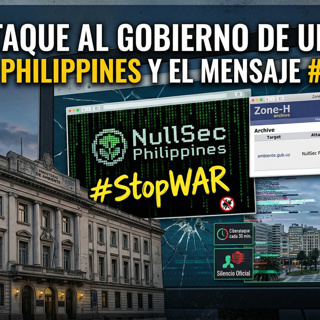
The hacktivist attack by NullSec Philippines is currently considered a "classic low-impact hacktivist defacement" that is "embarrassing but not catastrophic" for Uruguay's public sector. The immediate impact is limited to a web compromise of the Ministry of Environment site and an electronic sworn statement platform, where the attackers replaced the homepage with a splash page and dropped .txt proof files. There is currently no direct evidence of data exfiltration or backend infrastructure compromise.

Despite the limited technical scope, the attack impacts Uruguay's public sector security in several broader ways:

  • Compounding Existing Threats: The attack adds to the ongoing security burden of a government that already deals with constant probes—averaging one cyberattack every 30 minutes in 2024—and has suffered more severe incidents like the Paysandú ransomware attack.
  • Reputational Harm: Even as a cosmetic attack, it causes reputational damage to government entities and damages public trust in the state's ability to secure its digital infrastructure.
  • Risk of Escalation: If the vulnerabilities are not patched quickly, the defacement serves as a potential foothold for deeper access and could act as a test run for more severe breaches.
  • Lateral Movement: There is a persistent risk of undetected lateral movement within the network, meaning the attackers could use their current access to explore deeper into government systems.
  • Encouraging Future Attacks: Leaving the compromise unremediated could lead to increased targeting of the regional public sector by this group or others looking for easy targets.

Security analysts advise that this incident should be treated as a wake-up call. Uruguayan authorities need to fix the affected websites, actively check for lingering access, and monitor for any follow-up data leaks, which is the point at which this attack would escalate from "noise" into a severe security breach.

Denne episoden er hentet fra en åpen RSS-feed og er ikke publisert av Podme. Den kan derfor inneholde annonser.

Episoder(1035)

 UAlberta.ca Deep Dive: Institutional Technical Debt, Peer Apathy & The Cybermidnight Lens.

UAlberta.ca Deep Dive: Institutional Technical Debt, Peer Apathy & The Cybermidnight Lens.

Show Notes: In this 360-degree forensic deep dive, Alberto Daniel Hill unpacks the sprawling cybersecurity case study of uAlberta.ca—analyzing the 2023 BeeHive Systems vulnerability scan that uncovere...

7 Okt 1h 1min
Cas uAlberta.ca : Dette Technique Institutionnelle, Apathie des Pairs et l'Axe Cybermidnight.

Cas uAlberta.ca : Dette Technique Institutionnelle, Apathie des Pairs et l'Axe Cybermidnight.

Notes de l'Épisode : Dans cette analyse médico-légale à 360 degrés, Alberto Daniel Hill décortique le cas emblématique de la sécurité informatique de l'Université de l'Alberta (uAlberta.ca), en s'appu...

7 Okt 20min
Caso uAlberta.ca: Deuda Técnica Institucional, Apatía del Sector y el Enfoque Cybermidnight.

Caso uAlberta.ca: Deuda Técnica Institucional, Apatía del Sector y el Enfoque Cybermidnight.

Notas del Episodio: En este análisis forense integral de 360 grados, Alberto Daniel Hill desglosa el caso de ciberseguridad de la Universidad de Alberta (uAlberta.ca), examinando el informe de escaneo...

7 Okt 24min
Grabación Original: H1 - El Regreso Más Poderoso (Audio Raw Completo / X Space)

Grabación Original: H1 - El Regreso Más Poderoso (Audio Raw Completo / X Space)

🇪🇸 DESCRIPCIÓN EN ESPAÑOL (SPOTIFY)🎙️ Título del EpisodioGrabación Original: H1 - El Regreso Más Poderoso (Audio Raw Completo / X Space)Escucha la grabación íntegra y sin cortes del histórico X Spa...

29 Sep 3h 33min
Bandido Boss & The Fear Factory: Inside LATAM Cybercrime, Extortion SaaS, and Threat Manufacturing

Bandido Boss & The Fear Factory: Inside LATAM Cybercrime, Extortion SaaS, and Threat Manufacturing

🎙️ Spotify Episode TitleBandido Boss & The Fear Factory: Inside LATAM Cybercrime, Extortion SaaS, and Threat ManufacturingFrom multi-million dollar bank heists and cibernarco corridos to private thre...

29 Sep 52min
The Architecture of a Frame-Up

The Architecture of a Frame-Up

Show Title: The Architecture of Remorse — An Immersive Audio Drama by Alberto Daniel Hill[1][4]Episode Title: *EXTRA EPISODE — The Architecture of a Frame-Up (Progreso, Canelones · Tarantino Cut)*[2]S...

29 Sep 5min
MASTER DEEP DIVE — Alberto Daniel Hill's AI Architecture of Remorse: The Complete 5-Season Saga & Bonus Arcs

MASTER DEEP DIVE — Alberto Daniel Hill's AI Architecture of Remorse: The Complete 5-Season Saga & Bonus Arcs

EPISODE TITLE:MASTER DEEP DIVE — Alberto Daniel Hill's AI Architecture of Remorse: The Complete 5-Season Saga & Bonus ArcsWhat happens when a cybersecurity expert wrongfully jailed by the state turns ...

29 Sep 43min
EXTRA EPISODE — Progreso, Canelones: The Scapegoat Protocol

EXTRA EPISODE — Progreso, Canelones: The Scapegoat Protocol

FULL SHOW NOTES / DESCRIPTION:May 2026. A 19-year-old kid from Progreso, Canelones is arrested in a dawn raid. The headlines scream: "Leader of PampaLeaks Neutralized!" But behind the televised press ...

29 Sep 6min
Populært innen True crime

krimpodden-vg
avhort
krimarkivet-2
rss-avhort-aktuelt
podme-krim
rss-pa-innsiden-av-psychohoder
rss-svarttrost
rss-henlagt-andy-larsgaard
rss-espen-lee-usensurert
verdens-verste
rss-domt-2
forsvinningsfredag-podkast
krimpodden-orderud
kriminalkrniken
rss-domt-3
insiders
truecrimepodden-dokumentar
dodens-gard
rss-siktet
truecrimepodden-2